tag—Data Theft
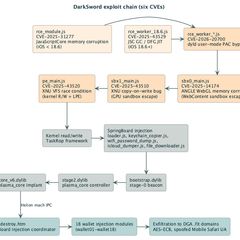 P7 DarkSword iOS Exploit Kit Adds Crypto Wallet Data Theft and Remote Commands
Cybersecurity researchers have disclosed details of a previously unseen variant of the DarkSword iOS exploit kit called P7 DarkSword. "Compared with the variants we usually observe, P7 reduces its on-device footprint, adds on-device keychain and crypto-wallet theft, and adds two way C2 communication with the attacker's infrastructure," iVerify said in a new report published Thursday. The name
 ARTEX AI Pentesting Tool Used in Data Theft Attacks on South Korean Financial Firms
Cybersecurity researchers have disclosed details of a targeted campaign aimed at South Korean financial organizations that used an artificial intelligence (AI) pen testing tool named ARTEX to carry out the attacks. The activity, per CrowdStrike Intelligence, was active from late September to early October 2026, and resulted in data exfiltration. "In this activity, the threat actor leveraged
 French Tax Data Theft Using Stolen Staff Passwords Went Undetected for Seven Weeks
An attacker used stolen passwords of staff at France's tax administration to take tax data on hundreds of thousands of taxpayers and businesses in June and July. Neither the tax administration nor France's national cybersecurity agency saw the data leave. The attack was not sophisticated, the agency, ANSSI, says in a report (in French) published on Tuesday: it worked because of weak
 Ghost Service Accounts Enable M365 Data Theft in Chile
Even if the organization locks down employee accounts, forgotten and lost service accounts can still undo the organization's entire M365 environment.
 ShinyHunters claims FBI hack, data theft in PeopleSoft zero-day breach
The ShinyHunters extortion gang claims it breached FBI systems using a new Oracle PeopleSoft zero-day vulnerability, gaining access to internal services and stealing sensitive data on employees and job applicants.
 CISA orders feds to patch Zyxel flaw exploited for data theft
Attackers are now actively exploiting a high-severity vulnerability in Zyxel GS1900 series switches, according to the U.S. Cybersecurity and Infrastructure Security Agency (CISA).
- Passkey-themed phishing attacks lead to Microsoft 365 data theft
Microsoft says threat actors linked to ShinyHunters, Helix, and other extortion gangs are using passkey and single sign-on-themed social engineering attacks to compromise corporate Microsoft accounts and steal data from Microsoft 365 services.
 Claude Used to Automate Exploitation and Data Theft Across Multiple Victims
Anthropic has warned that cybercriminals and state-sponsored hackers alike are using its Claude models for cyber attacks, weapons design, propaganda, and mass surveillance between December 2025 and August 2026. The threat actors, which the artificial intelligence (AI) company has branded Generative Threat Groups (GTGs), span state-sponsored groups, financially motivated criminals, commercial
 Fake IT Calls Target Executives in Microsoft 365 Data Theft and Extortion Attacks
Threat hunters have disclosed details of a widespread data theft and extortion threat cluster that's targeting Microsoft 365 and other software-as-a-service (SaaS) offerings through information technology (IT) help desk vishing, adversary-in-the-middle (AitM) token theft, and residential-proxy sign-ins. The activity, which mainly singles out directors, vice presidents, and other executive staff
 Berlin refuses to be blackmailed after network breach
Berlin’s state government has confirmed an extortion attempt following a data theft from its administrative network in August. Governing Mayor Kai Wegner and Interior Senator Iris Spranger addressed the extortion attempt on Friday, following an emergency Senate session at the Rotes Rathaus. “The state of Berlin is being blackmailed,” Wegner said. “Berlin has fallen victim to a serious crime.” He confirmed the city will not meet the attackers’ demands, and said the State Criminal Police

- 1
- 2
- 3
- 4
- 5
- 6
- 15