Microsoft is developing a new Edge security feature to reduce the attack surface by disabling the WebGL, WebGL2, and WebGPU APIs.
Inspired by Apple's Lockdown Mode, the new feature shares the same name and builds on Edge Enhanced Security Mode (also known internally as Super Duper Secure Mode), which disables Just-In-Time Compilation (JIT) from the V8 processing pipeline.
The new Edge Lockdown Mode offers optional, extreme protections for users facing highly targeted attacks who are willing to sacrifice website compatibility for stronger defenses.
"Lockdown Mode is designed for users who are at particular risk of being targeted in cybersecurity campaigns. This may include journalists, executives, security researchers, and administrators," said Partner Security Group Manager Gareth Evans.
"Individuals whose threat model justifies accepting reduced compatibility in exchange for stronger protection. It may also apply to devices operating within highly restricted environments."
Evans also warned that websites that use the disabled APIs (especially those with interactive graphics like games or maps) may not work as expected when this security feature is toggled on.
Edge users can test Lockdown Mode by switching to the Canary release channel, enabling the #edge-sdsm-plus flag, restarting the browser, then toggling on Strict mode for "Enhance your security on the web" and blocking WebGL graphics and WebGPU graphics.
After enabling it, users will see a new "Lockdown Enabled" indicator in the address bar when WebGL or WebGPU is blocked on a web page.
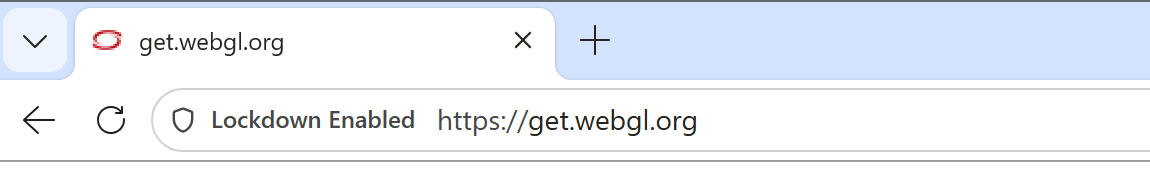
While the current Edge Canary Lockdown Mode blocks websites from using WebGL, WebGL2, and WebGPU APIs to stop attacks that try to escalate privileges and escape the sandbox, Microsoft plans to extend the feature in upcoming releases.
"The initial set of Lockdown Mode mitigations focus is the GPU process, a more privileged component that handles complex graphics workloads across browser code, third-party libraries, and device drivers," Evans added.
"Results from this experiment will inform the finished Lockdown Mode experience, including clearer descriptions of restricted capabilities and site-level exceptions that restore trusted sites without weakening protection everywhere else."
According to the company's estimates, this new security feature would have blocked around 60% of privilege escalation attacks targeting Edge users in the wild.
Last year, Microsoft also introduced a new Edge scareware sensor to ensure Defender SmartScreen blocks scam pages faster, and restricted access to Edge's Internet Explorer mode after learning that hackers were leveraging zero-day exploits in the Chakra JavaScript engine to access target devices.
Adaptive Security's AI agents analyze email intent, context, and behavior to uncover phishing, business email compromise, and invoice fraud.
See what's getting through with a 14-day read-only scan of Microsoft 365 or Google Workspace, with no MX changes.