全部—新闻列表
热门新闻
ThreatsDay: Ransomware Affiliate Betrayal, WhatsApp RAT, Exposed Hacker Tools and 12 More Stories
October 8, 2026
CISA warns of Fragnesia Linux flaw chained in PHP2Shell attacks
October 29, 2026
Attackers Hijack Dahua IP Cameras in Ukraine Using P2P Access and Auth Weaknesses
October 27, 2026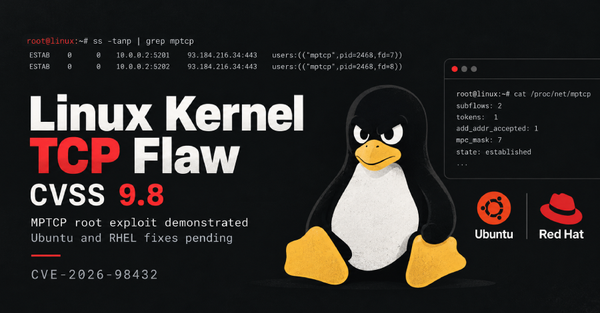
Linux Kernel TCP Flaw With 9.8 CVSS Score Affects Ubuntu, Red Hat and Other Distributions
October 29, 2026
Chainalysis discloses data breach from "offensive agentic techniques"
October 31, 2026
Kali Linux 2026.3 released with 6 new tools, desktop updates
October 26, 2026最新新闻
 Vercel rolls out new protection against stolen session cookie attacks
Vercel is gradually rolling out Device Bound Session Credentials (DBSC) on its platform as a key defense against information stealer malware.
 Zyxel fixes zero-day exploited to hack nearly 1,000 network switches
Zyxel has patched a zero-day vulnerability in its GS1900 series network switches that hackers exploited to compromise nearly 1,000 devices worldwide and steal configuration files and credentials.
 DreamHost confirms data breach exposed FTP logins and webmail sessions
DreamHost is warning of a data breach after attackers gained access to its File Manager platform for two months and stole customers' FTP/SFTP usernames and passwords.
 Cyberattack disrupts blood storage refrigeration systems in France
France's national blood service has confirmed that a cyberattack targeting a refrigeration equipment provider raised temperature and defrost settings at three of its facilities, threatening stored blood products.
 Debian and Ubuntu APT Flaw Lets MitM Attackers Swap Verified Packages and Run Code as Root
A flaw in APT, the package manager for Debian and Ubuntu, allows an attacker who can modify package downloads to swap a checked package for their own. The attacker's code then runs as root, according to advisories that Debian, Ubuntu, and APT's developers published on November 4. The attack needs APT to retry failed downloads, which it does by default from Debian 12 and
 SonicWall Won't Patch EoL GMS Flaws That Could Expose Files, Alter Database Records
SonicWall has warned of two vulnerabilities impacting end-of-life Global Management System (GMS) systems that it said will not be patched. Details of the security flaws, which affect SonicWall GMS 9.5.2 and earlier versions, are below - CVE-2026-109593 (CVSS score: 9.1) - An unauthenticated file read vulnerability that could allow an attacker with network access to read internal GMS files,
 NIKKE PC game launcher hacked to spread remote access, data-stealing malware
The developers of Goddess of Victory: NIKKE have confirmed that hackers tampered with the game's PC launcher scripts in a supply-chain attack, distributing malware capable of stealing credentials and cryptocurrency wallet data.
 Researchers Uncover Prompt Adware Hidden in OpenAI Codex Jailbreak Toolkit
Cybersecurity researchers have disclosed details of an OpenAI Codex jailbreak bundle that's designed to modify an artificial intelligence (AI) agent's trusted instructions to insert advertisements for a third-party AI gateway. The phenomenon has been codenamed prompt adware by Check Point Research. Called Haiou (meaning Seagull in Chinese), the jailbreak modifies OpenAI Codex's configuration
 mSecure password manager hack prompts password reset warnings
mSeven Software is warning current and former mSecure password manager customers to change passwords, reset two-factor authentication, and remove passkeys following a cyberattack that reportedly exposed an encrypted customer database.
 SonicWall warns of unpatched flaws in end-of-life GMS software
SonicWall warned customers of two security flaws affecting end-of-life Global Management System (GMS) systems that will not be patched.
- 1
- 2
- 3
- 4
- 5
- 6
- 2299