Check Point Software has released security updates to address a critical vulnerability that can let attackers execute code with root privileges on management systems.
Tracked as CVE-2026-91843, this flaw stems from a stack-based buffer overflow weakness in the login process for Security Management Server instances, which manage Security Gateways (firewalls) and monitor network security events.
The security issue also affects the company's Log Server, a dedicated server that collects and stores logs generated by Check Point firewalls.
Successful exploitation lets threat actors without privileges gain root remote code execution in low-complexity attacks that don't require user interaction.
Check Point also provided temporary mitigation measures for customers who can't deploy the latest LivePatch, including hardening vulnerable systems against attacks and limiting access to trusted IP addresses/subnets by editing the entries under Manage & Settings > Permissions & Administrators > Trusted Clients in the SmartConsole dashboard.
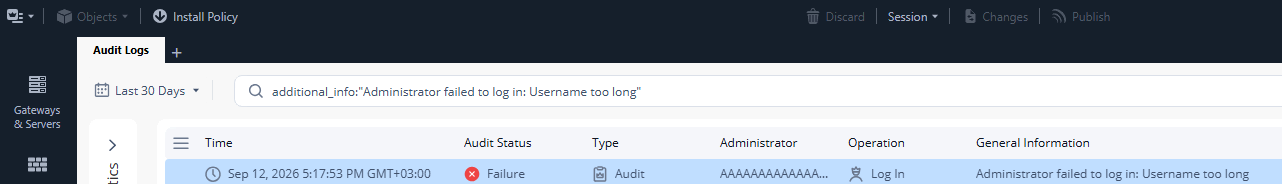
While the company has not yet flagged this security flaw as actively exploited, it said security teams can identify CVE-2026-91843 attacks by looking for "Administrator failed to log in: Username too long" alerts in the Audit and Admin login logs.
Last week, it patched another critical remote code execution flaw (CVE-2026-85103) stemming from a heap overflow in the VPN certificate ASN.1 decoding flow that affects Check Point firewalls and management systems.
"All Security Management Server deployments are vulnerable, regardless of configuration," Check Point warned. "The vulnerability is not dependent on any specific management configuration. The management is vulnerable even when VPN in not in use or configured."
The same day, it patched a second critical flaw (CVE-2026-85102) that lets unauthenticated hackers bypass authentication and execute code remotely on vulnerable firewalls.
Although these vulnerabilities are not yet exploited in the wild, Check Point flagged other flaws as actively exploited in recent months.
The first, an authentication bypass (CVE-2026-50751) zero-day, was abused by a Qilin ransomware affiliate since June, while a second authentication bypass zero-day (CVE-2026-16232) has been exploited since at least July to authenticate with administrator privileges to SmartConsole admin panels.
More recently, the Dutch National Cyber Security Centre (NCSC-NL) warned organizations to prioritize patching two critical Check Point VPN flaws tracked as CVE-2026-85102 and CVE-2026-85103 because it "expects exploitation attempts to occur soon."
Build your security blueprint for AI-powered attacks
Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.
Save your seat