A botnet of more than 1.3 million Android devices, mostly TV set-top boxes, lost control of its servers in late October in a takedown led by Google.
Google says it is highly confident that device maker Videostrong intentionally put a backdoor in the boxes and sold access to criminals.
They used the boxes for ad fraud and to pass other people's internet traffic through owners' home connections. The backdoor is still on the boxes, and owners cannot remove it themselves.
Videostrong, based in Shenzhen, China, makes Android TV boxes and other devices under its own name and for other brands. The backdoor, called x.cpe, was built into many device models and brands over several years. Google does not believe a rogue insider or a mistake was to blame.
Google used legal action to take down the domains and servers that controlled the botnet. It also took down the control domains of more than a dozen malware families loaded through the backdoor. Japan's National Police Agency, Lumen, HUMAN Security, Plume, Synthient and TrendAI worked with Google on the operation.
Because the criminals behind that malware also spread it in other ways, Google expects the action to cut off their access to at least 10 million more infected devices. It warns that backdoor operators and the criminals who buy from them quickly switch to new tools when one part of their setup is disrupted.
Google has cut ties with Videostrong. It banned the company, and any future subsidiaries or affiliates, from building or selling certified Android devices and from supplying software to other certified device makers.
What the Backdoor Did
The x.cpe backdoor runs as a system app inside the firmware, with system-level access, according to Google's analysis. It reports to the botnet's command-and-control (C2) servers and waits for orders. To install software silently, it first turns off the app checks in Google Play Protect, Android's built-in security feature.
Through the backdoor, the botnet's operators could install apps without the owner knowing, run commands, capture the screen and map the network the box sits on.
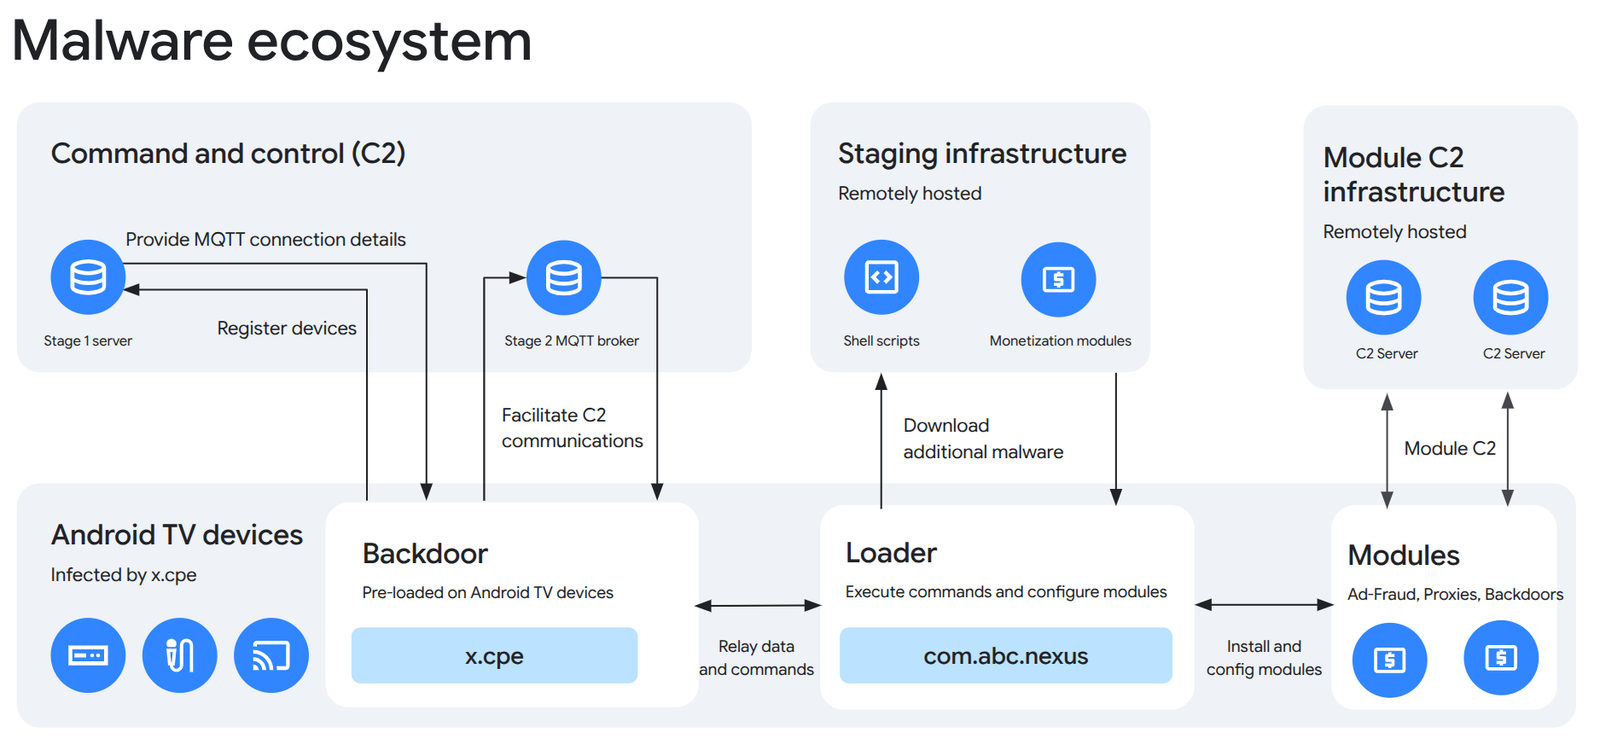
Google says it saw Videostrong's operators use some of these powers. They took live screenshots, sent keystrokes, copied out account details, device information, app lists and system logs, and opened reverse shells, which give a remote command line into the box.
Most of the criminals' modules, the add-on programs loaded through the backdoor, turned the boxes into residential proxies or sold their spare bandwidth. A residential proxy service sells access to a home internet connection, so a customer's traffic appears to come from an ordinary household. Other modules faked views of online ads.
Most infected devices are Android TV set-top boxes, but the backdoor also turned up on telehealth devices, karaoke machines and digital signage.
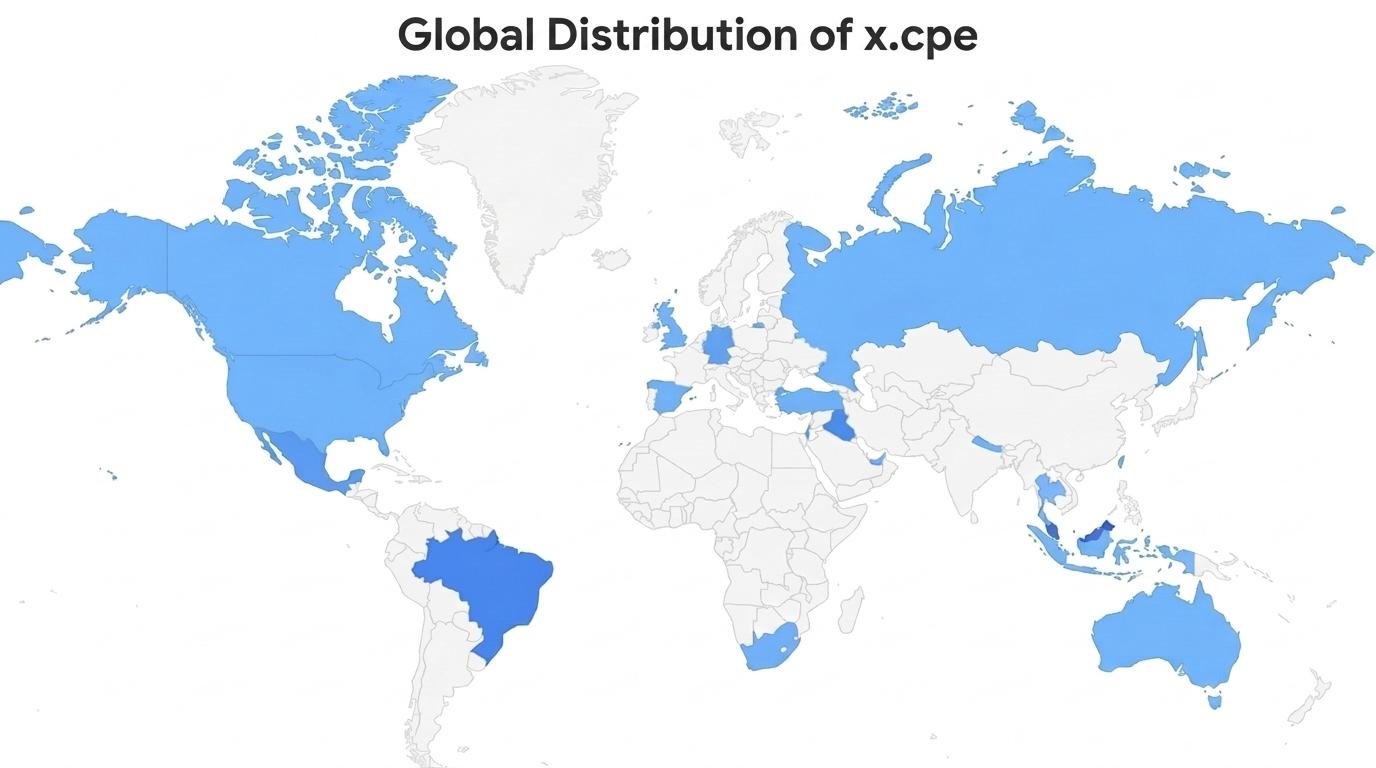
TrendAI, Trend Micro's enterprise business unit, counted 1,472,554 infected devices across 206 models between June 3 and October 1, and says the real number is at least that high. Malaysia, Brazil, Iraq, Mexico and Taiwan had the most. The U.S., Germany, the U.K., Australia and Canada each had about 26,000 to 42,000.
What Owners Can Do
Synthient, which tracks proxy networks and botnets, has published a list of 182 device model names seen in the campaign. The list warns that a model name alone does not confirm that a box is infected.
Synthient's report focuses on MECOOL-branded boxes, which it links to Videostrong. It bought a MECOOL KM9PRO Max and found the backdoor preinstalled. Plume, which makes Wi-Fi software for internet providers, found more than a dozen different devices using the botnet's control server, most of them from MECOOL.
Because x.cpe is part of the firmware, removing it does not stick. It reinstalls itself when the box restarts. TrendAI says the backdoor runs as a system app signed with the maker's key, so cleanup needs "vendor action, platform protection or replacement of the device."
Plume recommends a full factory reset, because the modules may have installed more backdoors, but it does not say whether a reset removes x.cpe itself. Synthient goes further, telling consumers to throw the boxes away for good because they pose a high risk of malware.
For organizations, Synthient recommends these steps:
- Use its published indicators to find MECOOL or similar devices on the network.
- Disconnect and throw away any that turn up.
- Block the control domains and IP addresses its report lists.
- Keep other smart devices on separate network segments, away from sensitive systems.
TrendAI advises companies with remote staff to treat unmanaged consumer devices on home networks as part of their attack surface, and to keep corporate access behind managed devices.
How Videostrong Was Identified
In Google's account, x.cpe passes settings from the C2 server to other Videostrong apps, including its YokaTV Player streaming app. One of the GitHub accounts that hosted the botnet's packages is named yf-videostrong.
Synthient, which worked with Google, also concluded with high confidence that Videostrong runs the operation. It points to a document signed by Videostrong's research and development director in an open folder on one of the botnet's servers, and to a Videostrong web domain that shares an IP address with the operators' control panel.
Plume found that Videostrong supplies both the firmware for these devices and tools to manage them remotely.
A Gap in Google's Device Tests
Google requires device makers to go through a set of compatibility and security tests. It says Videostrong hid its code to bypass a gap in those tests and loaded the malicious code after a device's first boot.
Google has changed its review process and is improving its checks of the firmware on certified Android TV devices.
As of November 2, Videostrong's own website listed products it calls "Google Certified Android TV Box" and "Google Certified Android TV Stick."
Plume says the botnet included both Google-certified devices and devices running the Android Open Source Project (AOSP) version. Google's report does not say how many certified devices were affected.
When Google sued over the BadBox 2.0 botnet in July 2025, the more than 10 million devices involved were uncertified.