South Korean police identified seven suspects linked to a cybercrime operation that breached more than 90 organizations in the country, with ARTEX AI pentesting framework used in most of the attacks.
According to local media citing the Seoul Metropolitan Police, the gang leader has a background in penetration testing and worked at a cybersecurity company between 2019 and 2022.
In 38 of the incidents, the threat actor demanded ransom payments of 360 million won ($270,000), promising in exchange not to leak stolen data.
Authorities believe the threat actor stole 8.2 million records from compromised organizations, including educational institutes, hospitals, large corporations, and even golf courses.
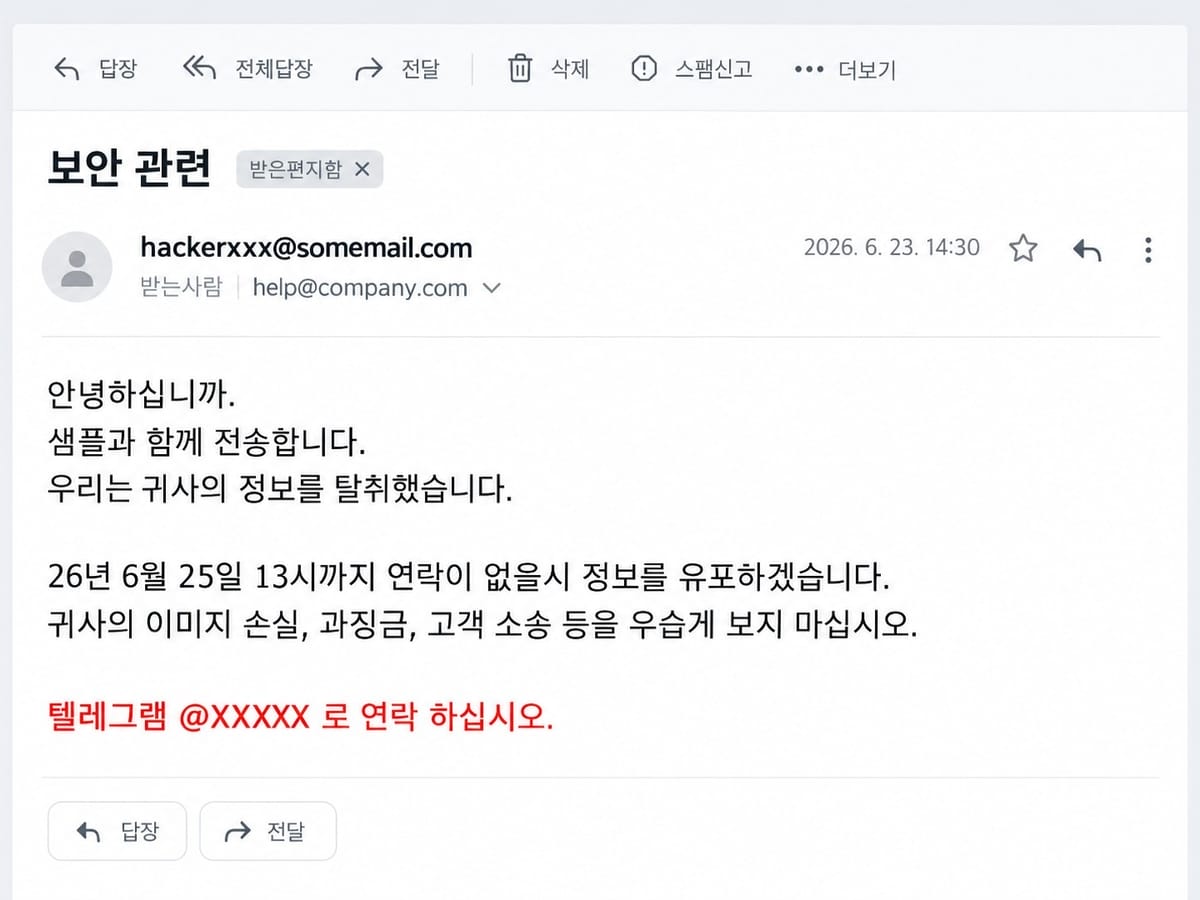
Yonhap News says that the gang leader is a self-taught 32 year-old hacker and started attacking organizations in September 2025.
The Seoul Metropolitan police told the publication that the hacker used the ARTEX AI penetration testing suite, the same autonomous framework used in the attacks against multiple South Korean banks attributed to a Chinese-speaking threat actor.
Initially, the hacker used conventional tools but adopted AI utilities in late August 2026 to expand the attacks.
Authorities arrested all seven suspects, but only the group’s leader remains in custody. Arrested on October 15, he was formally detained two days later and referred to prosecutors on October 23. The other six suspects remain under investigation without being detained.
Police opened a case after a victim filed a complaint in June, and investigators traced the suspects through server logs from the breached entities.
Law enforcement authorities reportedly used an in-house AI tool to analyze the recovered evidence.
The police told local media that AI has lowered the barrier to entry for aspiring cybercriminals, resulting in large-scale, high-impact incidents that were previously only possible for skillful, knowledgeable actors.
“This is the first case of arrest of a suspect in Korea related to a large-scale hacking and personal information theft crime that exploited generative AI," the police told Yonhap.
“Even individuals who are not professional hacker organizations can now hack on a large scale with the help of AI.”
The police continue the investigation, now focusing on whether any of the stolen data has been leaked on the dark web.
Once attackers have valid credentials, only 37% of their actions are blocked
Overall prevention scores can hide what happens after initial access. Once attackers are using valid credentials, prevention drops sharply.
The Blue Report 2026 measures defenses technique by technique across 338 million simulations run in customer production environments.
Get the report