A fake cryptocurrency trading app called Padre Terminal, previously available on the Apple App Store for iOS devices, has been linked to the theft of approximately $23,000 from 27 Solana wallets.
Blockchain investigator Iris confirmed that one victim was compromised through the malicious App Store app, but has not determined how the other affected wallets were compromised.
The researcher says the app drains wallets after unsuspecting users import their private keys into it.
Padre was a cryptocurrency trading platform, mainly used to buy and sell meme coins on Solana. It was later renamed Terminal by pump.fun, a platform focused on creating, buying, and selling cryptocurrency “meme coins” on the Solana blockchain.
Iris says the legitimate Padre trading service, now Terminal by pump.fun, is web-only, so any mobile apps impersonating it, including the one previously available on the App Store, are malicious.
At the time of BleepingComputer's initial investigation, we found two Padre apps on the App Store (ID 6802739263 and ID 6717572591). The former was the Iris-confirmed drainer app, while the latter is likely pump.fun's official app, live since October 2024.
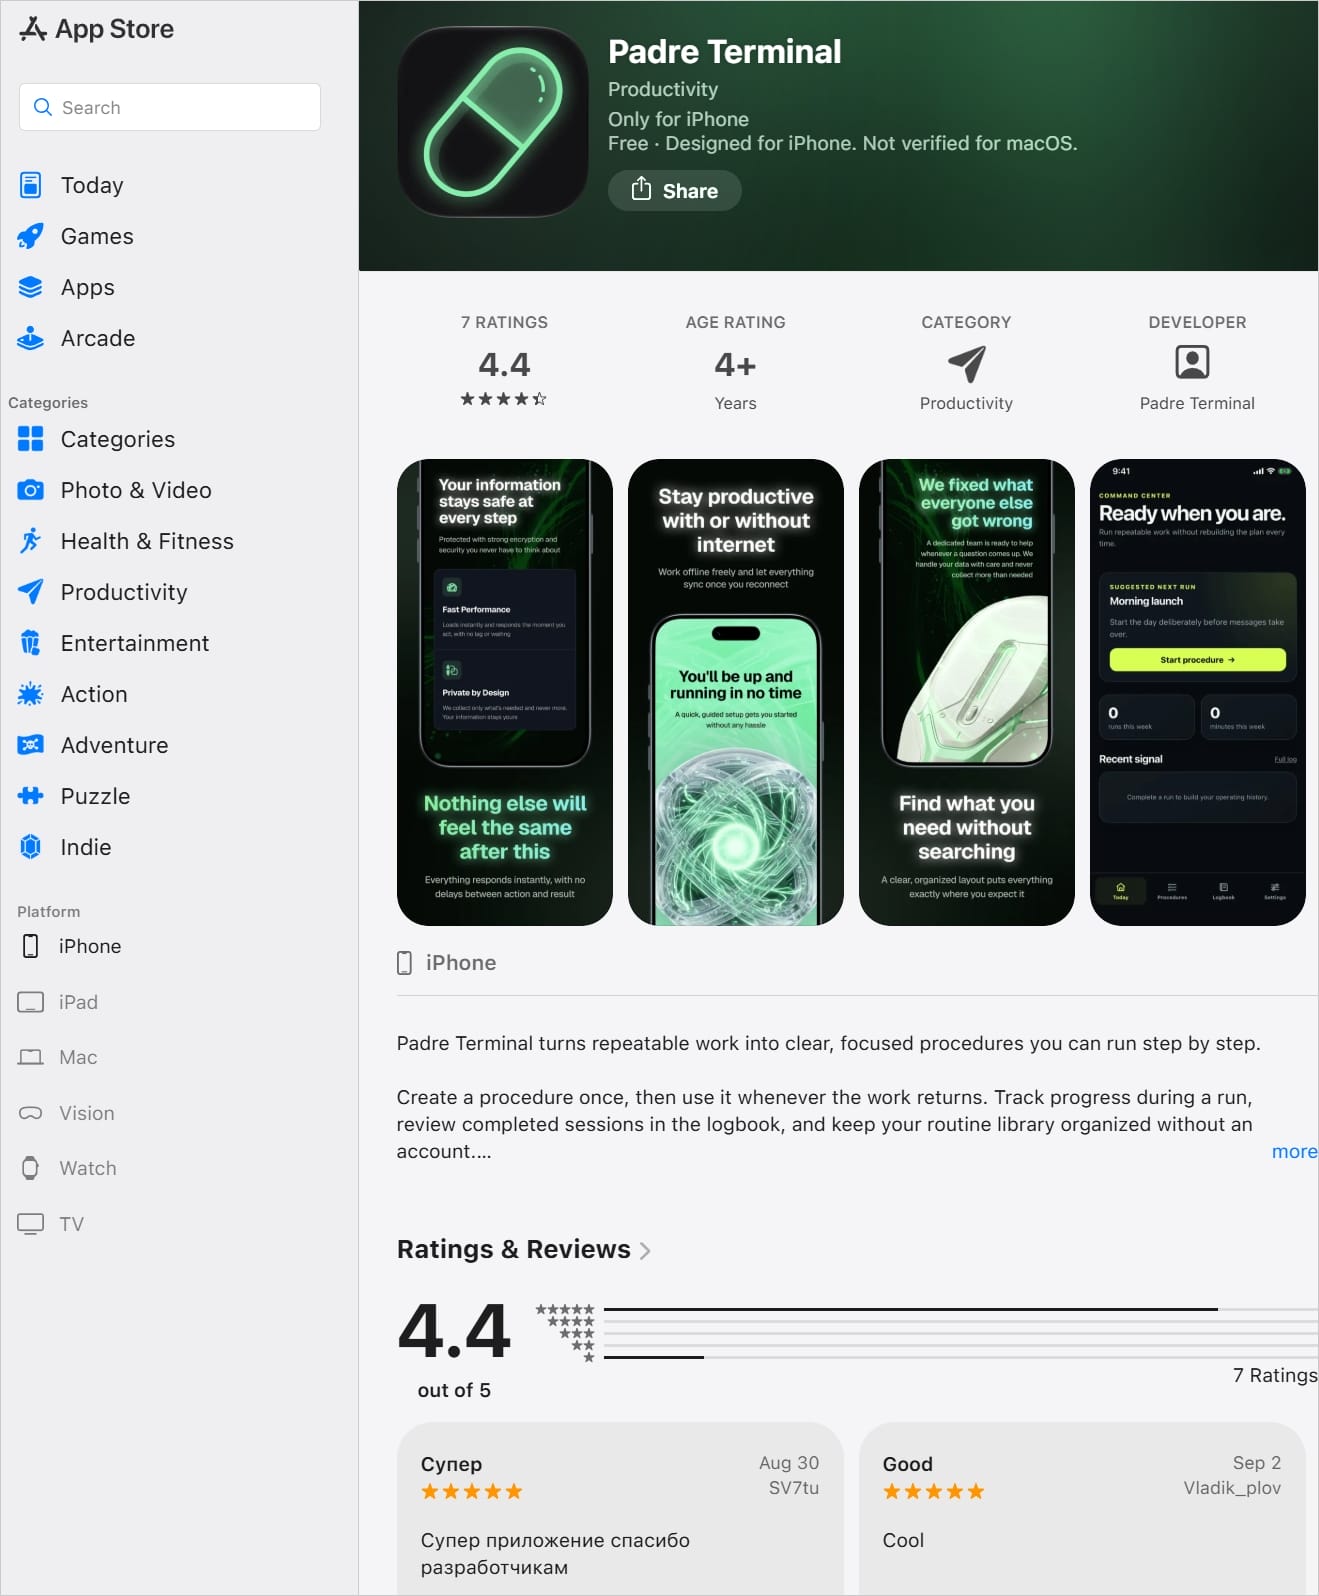
The malicious Padre Terminal app has since been removed from the App Store, with its listing now returning a 404 error.
Iris told BleepingComputer it suspects the trading interface of the fake app is served remotely, but has not directly observed the wallet-draining screen.
According to Iris, the operation has drained 27 Solana wallets since October 25, 2026, stealing approximately $23,000 in cryptocurrency. The stolen cryptocurrency was traced to the Solana address 3LAgKYoNenWrGWT3U4XWhpgVJWyYkP9wKpiPk8TJT1LN.
Iris says the attacker converted all remaining USDC (4,070 tokens) into SOL on October 29, eliminating the possibility of Circle freezing those funds.
The attacker then transferred 192 SOL to a new wallet (H84yazsUVCF8eJ6brh27rURMHjdKEVv2BuLS4iuUUQbu). According to Iris, the two wallets held a combined 229.66 SOL, with no funds cashed out at the time of the researcher's update.
The drainer remained active after the app's removal, with the latest reported theft occurring at 17:06 UTC on October 29.
More suspicious apps on the App Store
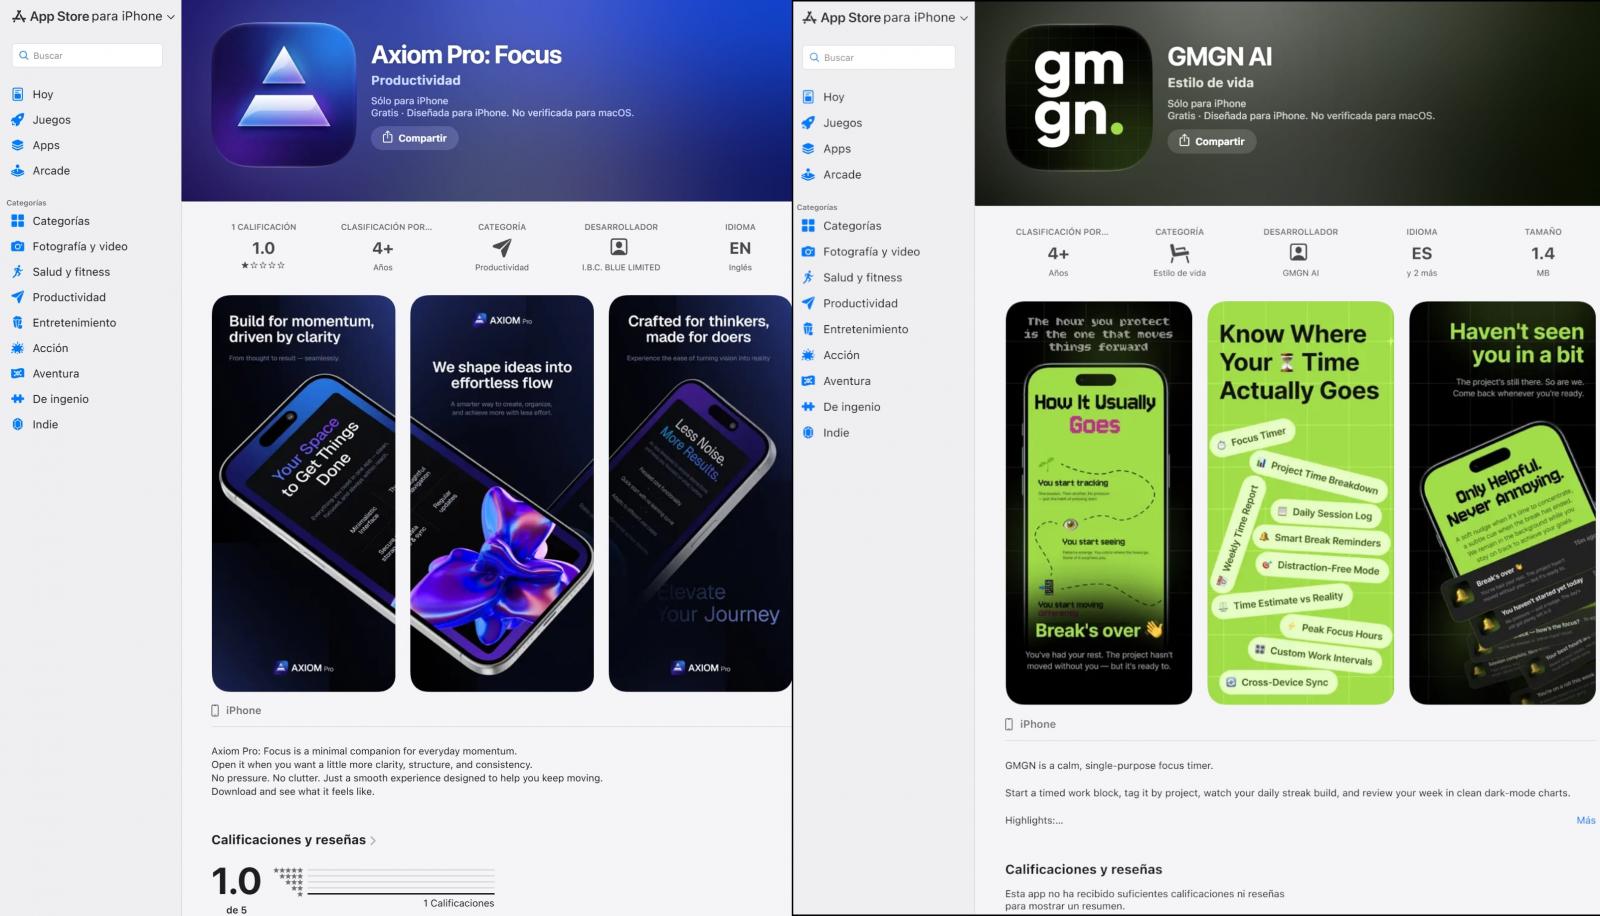
Iris identified at least five suspected crypto-brand impersonators on the App Store, including Padre Terminal, Axiom Pro: Focus, GMGN AI, HyperTerminal-HyperliquidTools, and Pump Fun Tokens & Analitycs.
Their listings feature seemingly harmless descriptions, but user reviews below sometimes reveal their true nature, with many exposing them for wallet theft and scams.
The Axiom Pro: Focus app, for example, had approximately 25 user reviews alleging wallet theft since February. One reviewer claimed the app had presented itself as a meme coin trading platform before changing into a focus application.
A review of the GMGN AI app alleged that $2,000 had been stolen, while a review associated with HyperTerminal-HyperliquidTools reported the theft of $2,020.
Another app, Pump Fun Tokens & Analitycs, presented itself as a notes application but had a review explicitly accusing it of stealing cryptocurrency.
Iris also found a script on the fake Axiom website containing backend addresses associated with Axiom, Aster, and GMGN impersonators, suggesting a common operator. However, Padre Terminal was not linked to that cluster.
Also, a script on the GMGN website blocks visitors from several CIS countries, potentially indicating that the attackers are attempting to avoid targeting users in those regions.
Iris has not independently confirmed cryptocurrency theft for the four suspicious apps.
BleepingComputer has contacted Apple about the Padre drainer and the other four suspicious apps available on the App Store, but we have not heard back as of publication.
In March 2024, a fake Leather cryptocurrency wallet app appeared on the Apple App Store, and multiple users reported losing their assets after connecting their wallets to it.
Apple eventually removed the app two weeks later and blocked the publisher from its developer program.
Users are recommended to follow links to the App Store from the projects' official websites and avoid installing apps with only a handful of downloads and reviews, or those published by entities with names that appear completely unrelated to the project.
Once attackers have valid credentials, only 37% of their actions are blocked
Overall prevention scores can hide what happens after initial access. Once attackers are using valid credentials, prevention drops sharply.
The Blue Report 2026 measures defenses technique by technique across 338 million simulations run in customer production environments.
Get the report