The U.S. Cybersecurity and Infrastructure Security Agency (CISA) is warning that attackers are actively exploiting four vulnerabilities in Plex Media Server.
The security issues are collectively called Plex2Shell. When chained in an exploit, an attacker can obtain the owner's admin token and execute code with elevated privileges.
Plex Media Server is a popular media suite that helps users organize personal collections of movies, TV shows, music, and photos, and stream them to other devices at home or remotely over the internet.
CISA has directed federal agencies to prioritize patching systems affected by Plex2Shell vulnerabilities or apply mitigations by October 23.
The security issues were discovered by security researcher Zach Main, who reported them responsibly to Plex on July 27.
The individual flaws are rated medium to high in severity, but the researcher assigns the full exploit chain a critical score of 9.8.
- CVE-2026-96652 – An SSRF flaw in /player/timeline that allows unauthenticated attackers to make Plex send POST requests to arbitrary destinations, including its own internal APIs.
- CVE-2026-96654 – A URL injection flaw in searchOne that allows attackers to invoke other plugins’ functions with attacker-controlled parameters.
- CVE-2026-96655 – An authenticated SSRF flaw in the transcoder endpoint that allows users to make Plex request arbitrary internal or external addresses.
- CVE-2026-96656 – An arbitrary file write flaw in the transcoder settings that allows administrators to plant malicious shared libraries that Plex subsequently loads, leading to code execution.
Zach Main published full technical details for the Plex2Shell vulnerabilities on October 16, followed by a proof-of-concept (PoC) exploit three days later.
On October 17, reports of Plex2Shell being exploited in the wild started to emerge, intially targeting Plex honeypots to deploy a cryptominer.
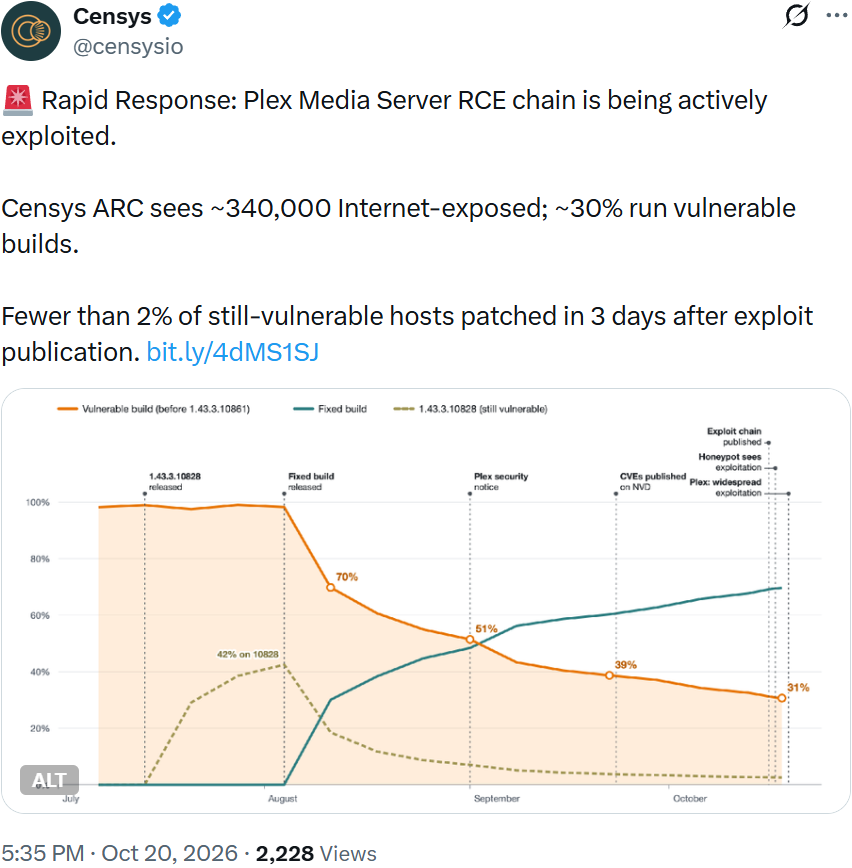
Plex2Shell impacts Plex Media Server versions before 1.43.3.10861, which was released on August 4.
Hackers also target Siemens Software Center
Alongside Plex2Shell, CISA has added to its catalog of Known Exploited Vulnerabilities (KEV) an uncontrolled search path element flaw, tracked as CVE-2026-110936, in Siemens Software Center (SSC).
The German technology giant warned on October 19 that hackers were leveraging the vulnerability in campaigns linked to a multi-payload ClickFix delivery platform called Romulus.
Recent research from operational technology (OT) cybersecurity company Forescout notes that Romulus "may be a privately operated panel, a commercial cybercriminal delivery service, an affiliate framework, or software that has been copied between operators."
Siemens's alert on CVE-2026-110936 shares indicators of compromise (IoCs) and advice on identifying compromised systems, urging administrators to update Siemens Software Center to version 4.0.9.8 or later.
CISA has also added CVE-2026-106931 to KEV, an OS command injection flaw that affects affecting the SiteGuard Server Edition web application firewall (WAF).
Both the vendor and Japan's CERT flagged CVE-2026-106931 as actively exploited late last week.
The vendor urged users to upgrade to SiteGuard Server Edition for Apache httpd, Nginx, and IIS version 8.00 Update 5, and SiteGuard Server Edition for Apache httpd and Nginx on FreeBSD version 7.00 Update 6 and later.
Once attackers have valid credentials, only 37% of their actions are blocked
Overall prevention scores can hide what happens after initial access. Once attackers are using valid credentials, prevention drops sharply.
The Blue Report 2026 measures defenses technique by technique across 338 million simulations run in customer production environments.
Get the report